Private AI Presentation Generators: Air-Gapped, Offline, and Self-Hosted Deployment
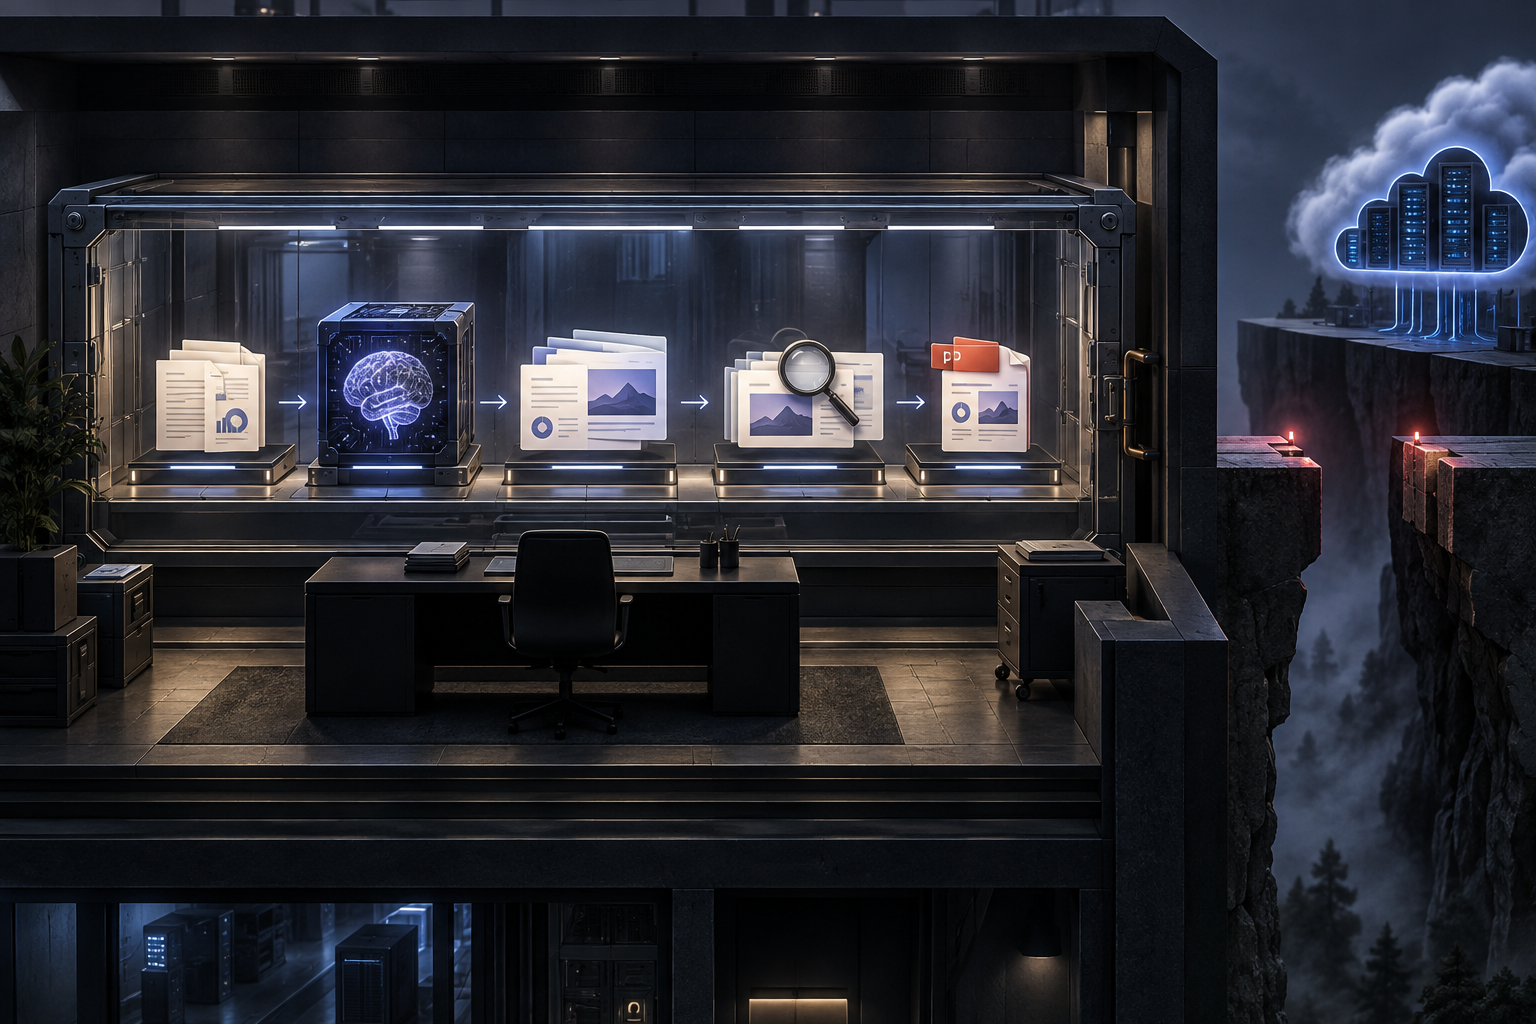
A private AI presentation generator keeps sensitive briefs, source documents, prompts, generated slides, and exports inside boundaries your organization controls. But “private” can describe very different architectures—from a self-hosted application that still calls a cloud model to a fully air-gapped stack with no external network path.
What is a private AI presentation generator?
A private AI presentation generator is software for creating decks with AI while giving the organization control over where information is processed, stored, transmitted, logged, and retained. The controlled information may include meeting notes, customer records, financial data, product roadmaps, research, regulated documents, proprietary templates, and the finished presentation itself.
The useful security question is not simply “Is it self-hosted?” It is: Which systems can see the content at every stage? A presentation workflow can cross several services before a PPTX is ready. A locally hosted user interface may still send the prompt to a hosted LLM, retrieve images from an external library, call web search, store telemetry in a SaaS platform, or write files to cloud object storage.
Private deployment is an architecture, not a label.Review the application, text model, image provider, document parser, search layer, storage, database, identity provider, observability stack, backup path, update mechanism, and export pipeline as one system.
Air-gapped vs. offline vs. self-hosted
These terms overlap, but they are not interchangeable. Use them precisely during security review and procurement.
| Deployment model | What it usually means | Best fit | Main caution |
|---|---|---|---|
| Self-hosted | The application runs in infrastructure you manage: on-premises, private cloud, or VPC. | Teams needing control over storage, networking, configuration, and integrations. | External model or media APIs may still receive content. |
| Offline | Core generation can run without a live internet connection, usually with local models and local assets. | Field work, travel, unreliable connectivity, labs, and privacy-sensitive individual use. | Updates, collaboration, and large-model performance require planning. |
| Air-gapped | The production environment has no direct connection to untrusted networks, and data movement uses controlled transfer procedures. | Classified, critical-infrastructure, defense, sovereign, and highly restricted environments. | Every dependency, model, font, asset, update, and export path must work inside the boundary. |
A VPC deployment is not automatically air-gapped. An offline desktop app is not automatically enterprise-governed. A self-hosted application is not automatically private if its configured AI providers receive the organization’s source material. The correct description depends on the actual network and data flow.
Map the complete presentation data path
Start with one representative workflow: a user uploads a confidential PDF, asks for a board presentation, applies a corporate template, generates diagrams and images, edits the result, and exports a PPTX. Follow that request from the first byte to the final file.
01 · INPUTSource boundary
Prompts, uploads, URLs, connected drives, CRM data, databases, and approved internal repositories.
02 · PROCESSGeneration boundary
Text models, embeddings, parsers, image generation, search, rendering, and temporary working files.
03 · OUTPUTReview boundary
Preview links, editable PPTX, PDF, images, notes, citations, logs, backups, and sharing controls.
Questions for every component
- Does content leave the controlled environment? If yes, exactly what is sent and to which endpoint?
- Where are prompts, uploads, intermediate files, generated images, and exports stored?
- What appears in application, model, proxy, audit, error, and observability logs?
- How are encryption keys, model credentials, service accounts, and secrets managed?
- What is retained, for how long, and how is deletion verified across replicas and backups?
- Can administrators restrict providers, models, templates, integrations, and outbound domains?
If you cannot draw the data path, you cannot make a defensible privacy claim about the presentation workflow.
What a real air-gapped deployment requires
Air-gapped operation changes more than the LLM endpoint. The environment must contain every dependency needed to create and export a usable deck. Anything that silently relies on the public internet becomes a failure point.
Local models and model artifacts
Download and approve model weights, tokenizers, runtimes, and GPU dependencies before they enter the isolated environment. Record licenses, checksums, provenance, security review, and the hardware profile required for acceptable latency. Treat model updates as controlled software releases.
Local images, icons, fonts, and templates
A slide generator often reaches for stock photography, icon libraries, web fonts, or hosted image-generation services. Replace those calls with approved internal asset libraries, self-hosted image generation, curated templates, and locally installed fonts. Test fallbacks so the system does not produce empty or broken slides when an external asset is unavailable.
Offline document parsing and rendering
PDF extraction, Office-file parsing, browser rendering, chart generation, and PPTX/PDF export must all execute inside the boundary. Test difficult documents, large decks, unusual fonts, charts, tables, and images—not only a simple five-slide demo.
Controlled updates and transfer
Define how containers, operating-system patches, model weights, templates, and security fixes enter the environment. Use signed artifacts, malware scanning, documented approval, immutable versioning, and rollback. Define the reverse path too: who can export a deck, through which media or gateway, with what inspection and audit record.
A practical reference architecture
A defensible private presentation stack usually separates the user-facing application from generation services and data systems. Exact products will vary, but the boundaries are consistent.
- Identity and accessConnect enterprise identity where appropriate, enforce roles, separate administrators from authors, and apply least privilege to projects, templates, providers, and exports.
- Presentation applicationRun the web or desktop interface inside the approved environment. Disable user-controlled provider changes when central policy requires fixed endpoints.
- Model gatewayRoute generation to approved local models, an OpenAI-compatible internal endpoint, or a private managed-model endpoint. Apply allowlists, quotas, request logging policy, and version control.
- Content servicesKeep document parsing, retrieval, embeddings, search, image generation, icons, fonts, and templates inside the same trust boundary—or explicitly document each exception.
- Data layerUse approved databases and object storage, encrypt data at rest and in transit, define project isolation, and test retention, backup, restore, and deletion.
- Export and reviewRender slides, check overflow and visual defects, preserve editability, scan exported files, and require human approval before external sharing.
Deployment roadmap: from pilot to controlled production
1. Classify the presentation workload
Choose a real but non-production example. Identify the data classification, users, source systems, required templates, output formats, collaboration needs, and approval path. Avoid proving only that the software starts; prove that the end-to-end workflow fits policy.
2. Select the smallest sufficient isolation model
Some teams need self-hosting with approved cloud models. Others need private endpoints and customer-controlled storage. A smaller group needs fully local models and zero internet access. Stronger isolation raises operational responsibility, so match controls to risk instead of using “air-gapped” as a prestige feature.
3. Build a dependency inventory
List containers, packages, model weights, fonts, templates, image assets, databases, browser/rendering components, licenses, certificates, and update sources. Record owners and approved versions.
4. Apply policy before onboarding users
Configure authentication, roles, provider restrictions, secret management, storage locations, network egress, logs, retention, backups, and export controls. Give users clear guidance about which information may enter the system.
5. Test failure and recovery
Disconnect the network. Remove a model endpoint. Fill storage. Restart a generation job. Restore from backup. Rotate a credential. Upgrade and roll back. Confirm that the application fails safely and that partial files do not expose sensitive content.
6. Validate presentation quality
Privacy does not compensate for unusable output. Measure outline accuracy, factual traceability, template fidelity, text overflow, image relevance, chart correctness, editability, PPTX/PDF parity, generation time, and reviewer effort.
Private AI presentation generator evaluation checklist
| Area | Evidence to request | Pass condition |
|---|---|---|
| Deployment | Architecture diagram, supported topologies, ports, dependencies | Matches the approved on-prem, VPC, offline, or air-gapped boundary |
| Models | Provider list, local-model support, endpoint configuration | Only approved endpoints can receive content |
| Data | Storage map, retention settings, backup and deletion procedure | Data lifecycle is controlled and testable |
| Network | Egress list, DNS requirements, proxy behavior, offline test | Undocumented outbound traffic is blocked |
| Identity | Authentication, roles, session policy, audit events | Least privilege and accountable administration |
| Supply chain | SBOM, signatures, checksums, vulnerability process | Artifacts can be verified before import |
| Output | Representative PPTX/PDF, malware scan, editability test | Files are safe, editable, and reviewable |
| Operations | Monitoring, recovery, upgrades, rollback, support model | The team can run the service without hidden cloud dependencies |
Ask vendors and internal platform teams to demonstrate these controls with a representative brief. A policy document is useful; a repeatable test is stronger.
Where Presenton fits
Presenton is an open-source AI presentation generator that can run through Docker or as a desktop application. The project supports editable PowerPoint and PDF output, reusable presentation templates, a presentation API, configurable AI providers, OpenAI-compatible endpoints, and local-model options such as Ollama and LM Studio.
That flexibility allows teams to choose between a managed cloud workflow, customer-controlled infrastructure, local desktop use, and more restricted private deployments. The privacy result still depends on configuration. For example, a self-hosted Presenton instance connected to an external LLM or image provider is not equivalent to a fully offline stack.
For strict isolation: keep the Presenton application, model endpoints, image pipeline, asset libraries, storage, database, and rendering/export services inside the controlled environment; disable unapproved provider changes and external search; and validate the full workflow with network egress blocked.Presenton’s official Docker API guide documents local container deployment, while the open-source repository lists provider and deployment configuration. Enterprise teams should pair those technical capabilities with their own identity, network, logging, retention, backup, and change-management controls.
The bottom line
A private AI presentation generator is not defined by where its interface runs. It is defined by the complete path taken by documents, prompts, model requests, assets, temporary files, logs, and exports.
Self-hosting gives teams infrastructure control. Offline operation removes a live-internet dependency. Air-gapping adds a hard network boundary and a disciplined process for moving software and data across it. Choose the least complex model that satisfies policy, then verify it with a real deck, blocked egress, failure tests, and a human review gate.
Published on August 17, 2026
Curious about something?
Find quick answers to common questions about the platform, pricing, and security.
No. A self-hosted application may still send prompts, documents, images, search queries, telemetry, or logs to external services. Verify the full data path and configured providers.
Offline means the workflow can operate without a live internet connection. Air-gapped means the production environment is intentionally isolated from untrusted networks and uses controlled procedures for importing updates and exporting data.
Yes, if the environment contains approved local models, document parsers, fonts, templates, image or asset sources, rendering components, and PPTX/PDF exporters. External dependencies must be replaced or mirrored internally.
Presenton documents support for local and configurable model endpoints, including Ollama, LM Studio, and OpenAI-compatible APIs. The exact privacy boundary depends on the selected text, image, search, storage, and logging configuration.
Use one representative confidential-style brief with synthetic data. Block outbound network access, inspect logs and storage, generate and export the deck, test deletion and recovery, and verify that the output remains editable and reviewable.
Got Anymore Questions?
Get Help