How to Embed AI Presentation Generation in a SaaS Product: API, Architecture, and Security
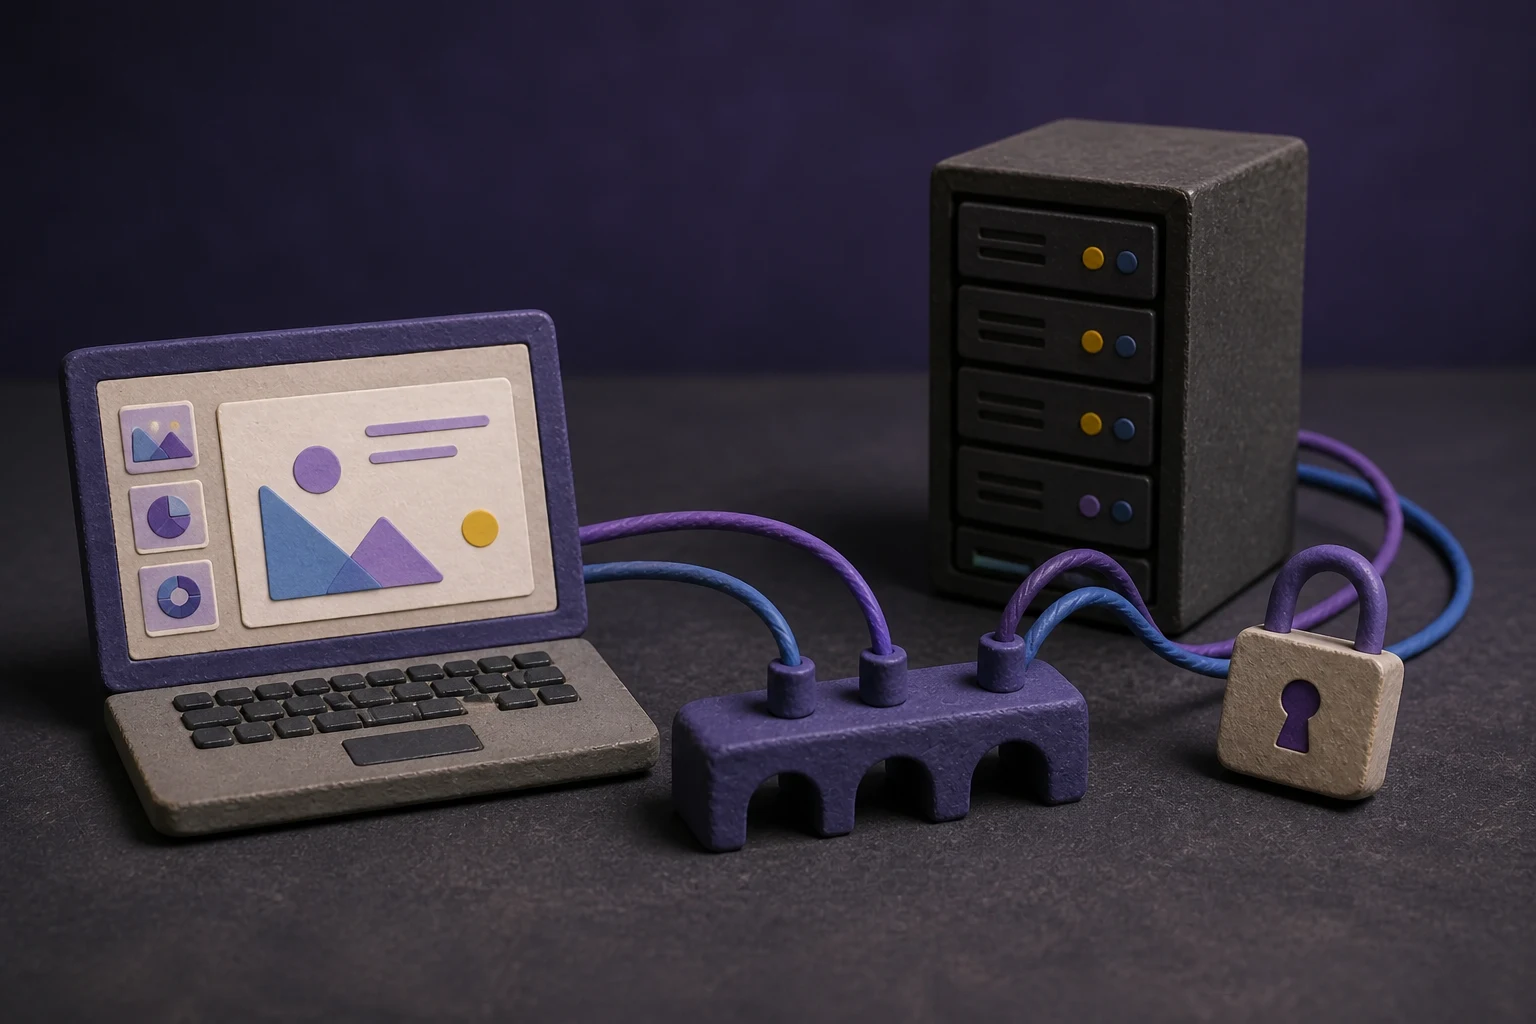
To embed AI presentation generation in a SaaS product, treat it as an asynchronous document workflow: collect authorized inputs, create a structured generation job, route it to an approved model and renderer, store an editable output, and return status and review controls to the host product. The API boundary should make data handling, tenant isolation, retries, and human approval explicit.
What is the best architecture for an AI presentation API?
The most reliable pattern is a job-based API behind the customer’s existing authentication and authorization layer. The SaaS product owns the user experience, tenant permissions, source selection, and delivery. The presentation service owns generation, layout, asset handling, and editable export.
An embedded AI presentation workflow should accept structured instructions and approved source content, process the job within a declared data boundary, return an auditable job status, and produce an editable presentation that a person can review before delivery.
What should an embedded presentation-generation API include?
A useful API contract is small enough for developers to adopt but explicit enough for security and platform teams to review. Keep generation requests versioned and make defaults visible rather than hiding important behavior in a dashboard.
Core request fields
- Source inputs: document IDs, structured data, approved URLs, or text supplied by the host product.
- Presentation brief: audience, objective, language, slide count range, tone, and required sections.
- Template: a tenant-approved template or a product-managed template version.
- Model and processing policy: the allowed model route, region, retention behavior, and external dependency policy.
- Delivery settings: editable PPTX, PDF preview, web preview, webhook, or an internal asset reference.
Core response fields
Return a stable job ID, status, timestamps, warnings, source lineage, output references, and an error code that a host application can act on. Avoid returning only a binary file: customers need to know whether the file is still processing, needs review, or failed because an input was unavailable.
How do you secure AI presentation generation inside a SaaS product?
Security starts at the tenant boundary and continues through every source, model, asset, export, and webhook. An API key alone does not prove tenant isolation or private processing.
For regulated or confidential workflows, obtain security and privacy review before promising a deployment model. Describe the proposed architecture precisely and avoid broad claims such as “the AI is secure” without evidence.
How should teams design the embedded user experience?
Users should understand what will be generated, from which sources, under which template, and what happens next. A good experience makes review visible rather than implying that an AI-generated deck is final.
- Choose the workflow: start from a report, account, project, brief, or document set.
- Confirm scope: show the selected sources, date range, audience, template, and output type.
- Generate asynchronously: provide progress and allow the user to continue working in the host product.
- Review warnings: surface missing sources, unsupported claims, layout issues, and content that needs confirmation.
- Edit and approve: preserve editable slide output and record who approved or exported it.
Start with one repeatable workflow—such as a QBR, proposal, project status report, or customer briefing—before exposing a general-purpose “generate anything” button.
Build an AI presentation layer or integrate one?
Building gives a product team control over the end-user experience and domain-specific orchestration. Integrating an existing presentation engine can reduce the work required for layout, templates, editable export, model routing, and document handling. The right decision depends on where the product’s differentiation lives.
Embedded AI presentation API launch checklist
- Version the API and define idempotency, retries, timeouts, and cancellation.
- Test tenant isolation with adversarial cross-tenant IDs and expired permissions.
- Measure factual corrections, layout defects, export failures, review time, and job completion.
- Validate the full data path for text, documents, images, fonts, model calls, storage, logs, and telemetry.
- Provide an editable output and a documented human-review workflow.
- Publish example requests, error codes, rate limits, webhook signatures, and deletion behavior.
Planning an AI presentation feature?
Review the API boundary, data flow, editable output, and approval model before committing to a pilot.
Discuss your workflow
Design the AI presentation API around a clear job contract
A dependable integration begins with a stable job contract. The request should identify the tenant, user, authorized sources, template, output formats, callback or polling preference, and an idempotency key. The response should return a job ID and an explicit state model such as queued, processing, needs review, completed, failed, or expired.
Tenant isolation must apply to source files, prompts, generated assets, templates, logs, and download links. Use authorization checks when a job is created and again when its status or files are retrieved. Short-lived download URLs, predictable deletion rules, and audit events make the workflow easier to operate and explain to customers.
Reliability matters as much as generation quality. Queue long-running work, retry only safe operations, preserve failure reasons, enforce file and token limits, and make webhook delivery repeatable. Treat the generated deck as a draft until a person or a customer-defined rule approves it. That keeps the embedded AI presentation feature useful without hiding important decisions inside an opaque background process.
Where Presenton fits in a SaaS product architecture
Presenton is a useful reference point for SaaS teams designing presentation generation as a product capability: the host application should collect authorized inputs, create a generation job, apply tenant and template rules, return an editable output, and preserve a review step. Treat the integration as a document workflow with explicit states rather than as a synchronous text-completion call.
Before launch, test tenant isolation across source files, prompts, generated assets, templates, logs, and download links. Also test idempotency, retries, webhooks, deletion, permissions, and failed rendering. The best integration is the one customers can understand and administrators can operate.
Presenton references and next steps
The product details in this guide are grounded in Presenton’s current public documentation and enterprise overview. Presenton documents a template-based workflow, REST API generation and editing, editable PPTX/PDF export, configurable model providers, and self-hosted deployment options. Deployment-specific controls should still be confirmed for the configuration your organization will operate.
- Presenton enterprise overview — deployment, identity, storage, templates, API, and enterprise workflow capabilities.
- Presenton documentation — product setup, self-hosting, supported providers, and generation workflow.
- Presenton API introduction — template-based generation, editing, export, and application integration.
For the best internal-link path, continue to the related enterprise guide above, review the enterprise evaluation checklist, and then Discuss your workflow with the Presenton team.
Published on August 17, 2026